
Your systems hold sensitive data and carry operational risk. We help define security controls, test exposure and document the evidence.
Security & Governance for systems your organisation depends on

Official OEM Partners: Sophos & Fortinet
Security & Governance connects technical controls with the people and evidence needed to operate them. It covers firewall and endpoint protection, authorised security testing, data loss prevention and the engineering behind AML workflows.
Sparkr Digitals helps organisations scope security controls around their systems, data and obligations. We work across OEM security solutions, threat assessments, DLP and AML engineering, with clear boundaries for each engagement.
Identity & RBAC / DLP & Encryption / VAPT Audits / AML Compliance / Sophos & Fortinet OEM
Security & Governance services
Four services, clear control ownership.
Start with your exposure, data or compliance workflow. We help define the controls, assessment scope and evidence the engagement needs.
 Cybersecurity OEM solutionsSophos and Fortinet next-gen firewalls and endpoint protection, scoped around your network and operating requirements.View service
 VAPT & threat assessmentsWritten-scope testing to identify exposure, document evidence and prioritise remediation across agreed systems.View service
 Data loss prevention (DLP)Policies and controls for how sensitive information is accessed, transferred and shared across your organisation.View service
 AML & compliance engineeringScreening, monitoring and reporting workflows with traceable decisions your regulator can audit.View service
 Not sure which one?Tell us which systems, data or obligations need attention. We will help define a focused security or governance engagement.Ask us
Where to start
Controls, testing, data or AML workflows?
Three questions to identify the control gap and the right starting scope.
Selected work
Selected design and software work, not security audit results
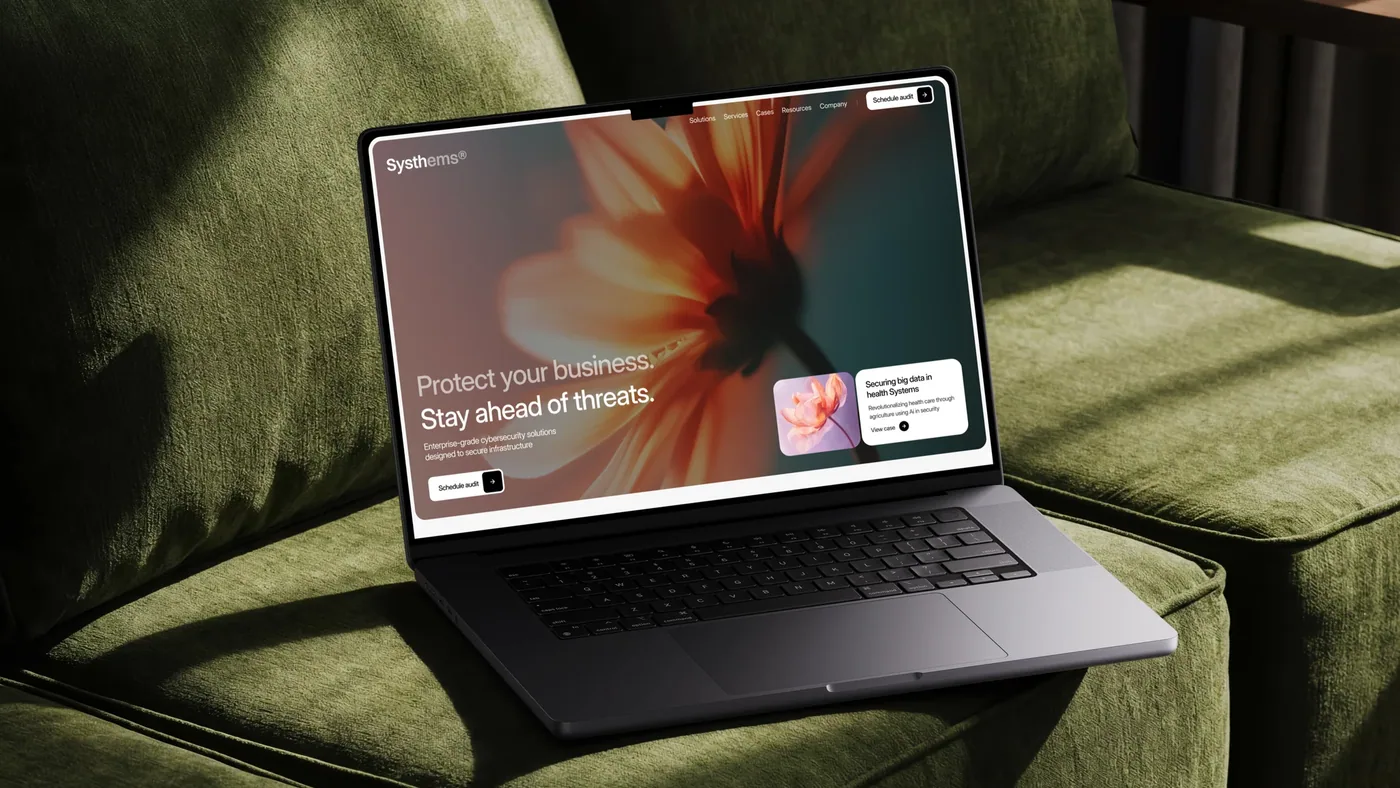 Independent concept
Systhems: an independent cybersecurity website concept.
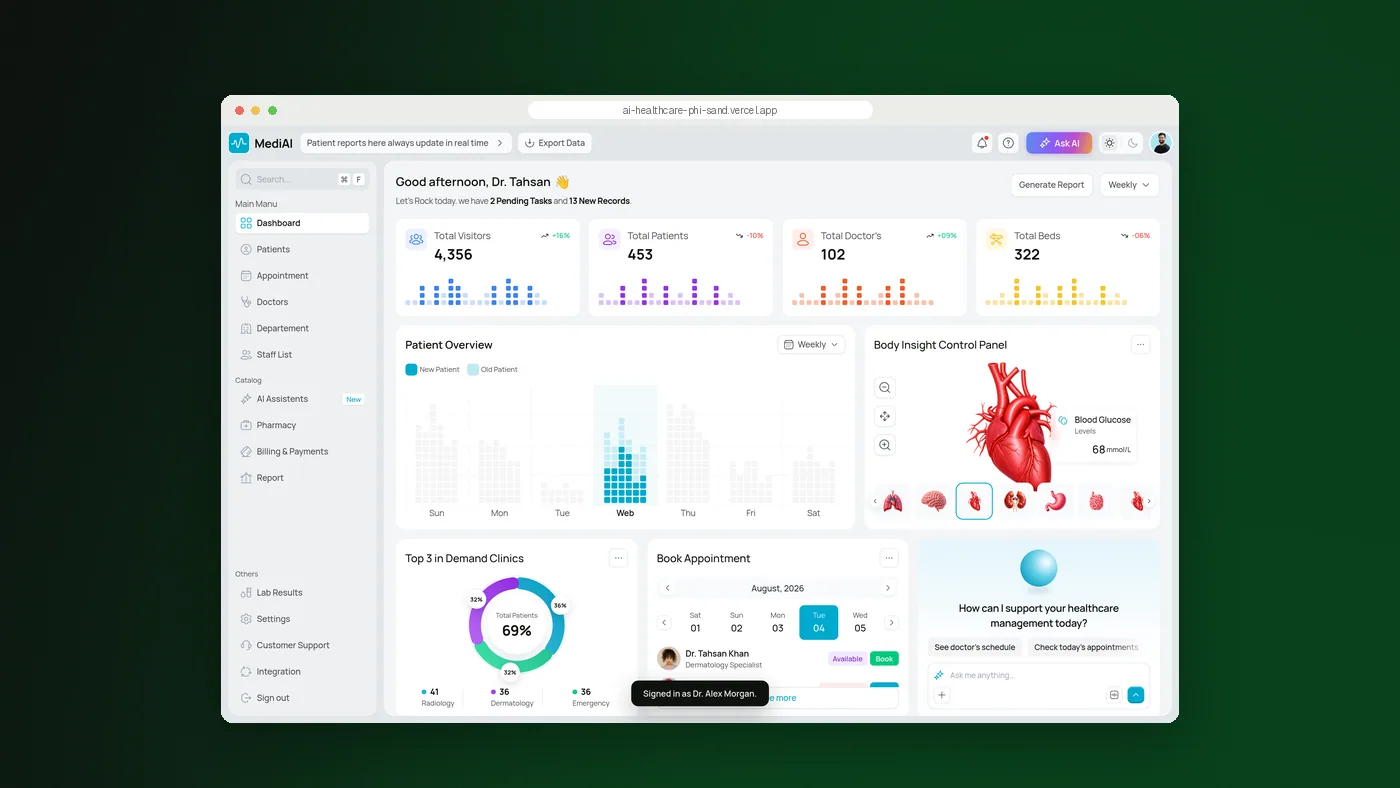 Interface prototype
MediAI: patient context and scheduling in a clinical workspace.
 Design & web app
Relix CRM: leads, deals and invoicing in one workspace.
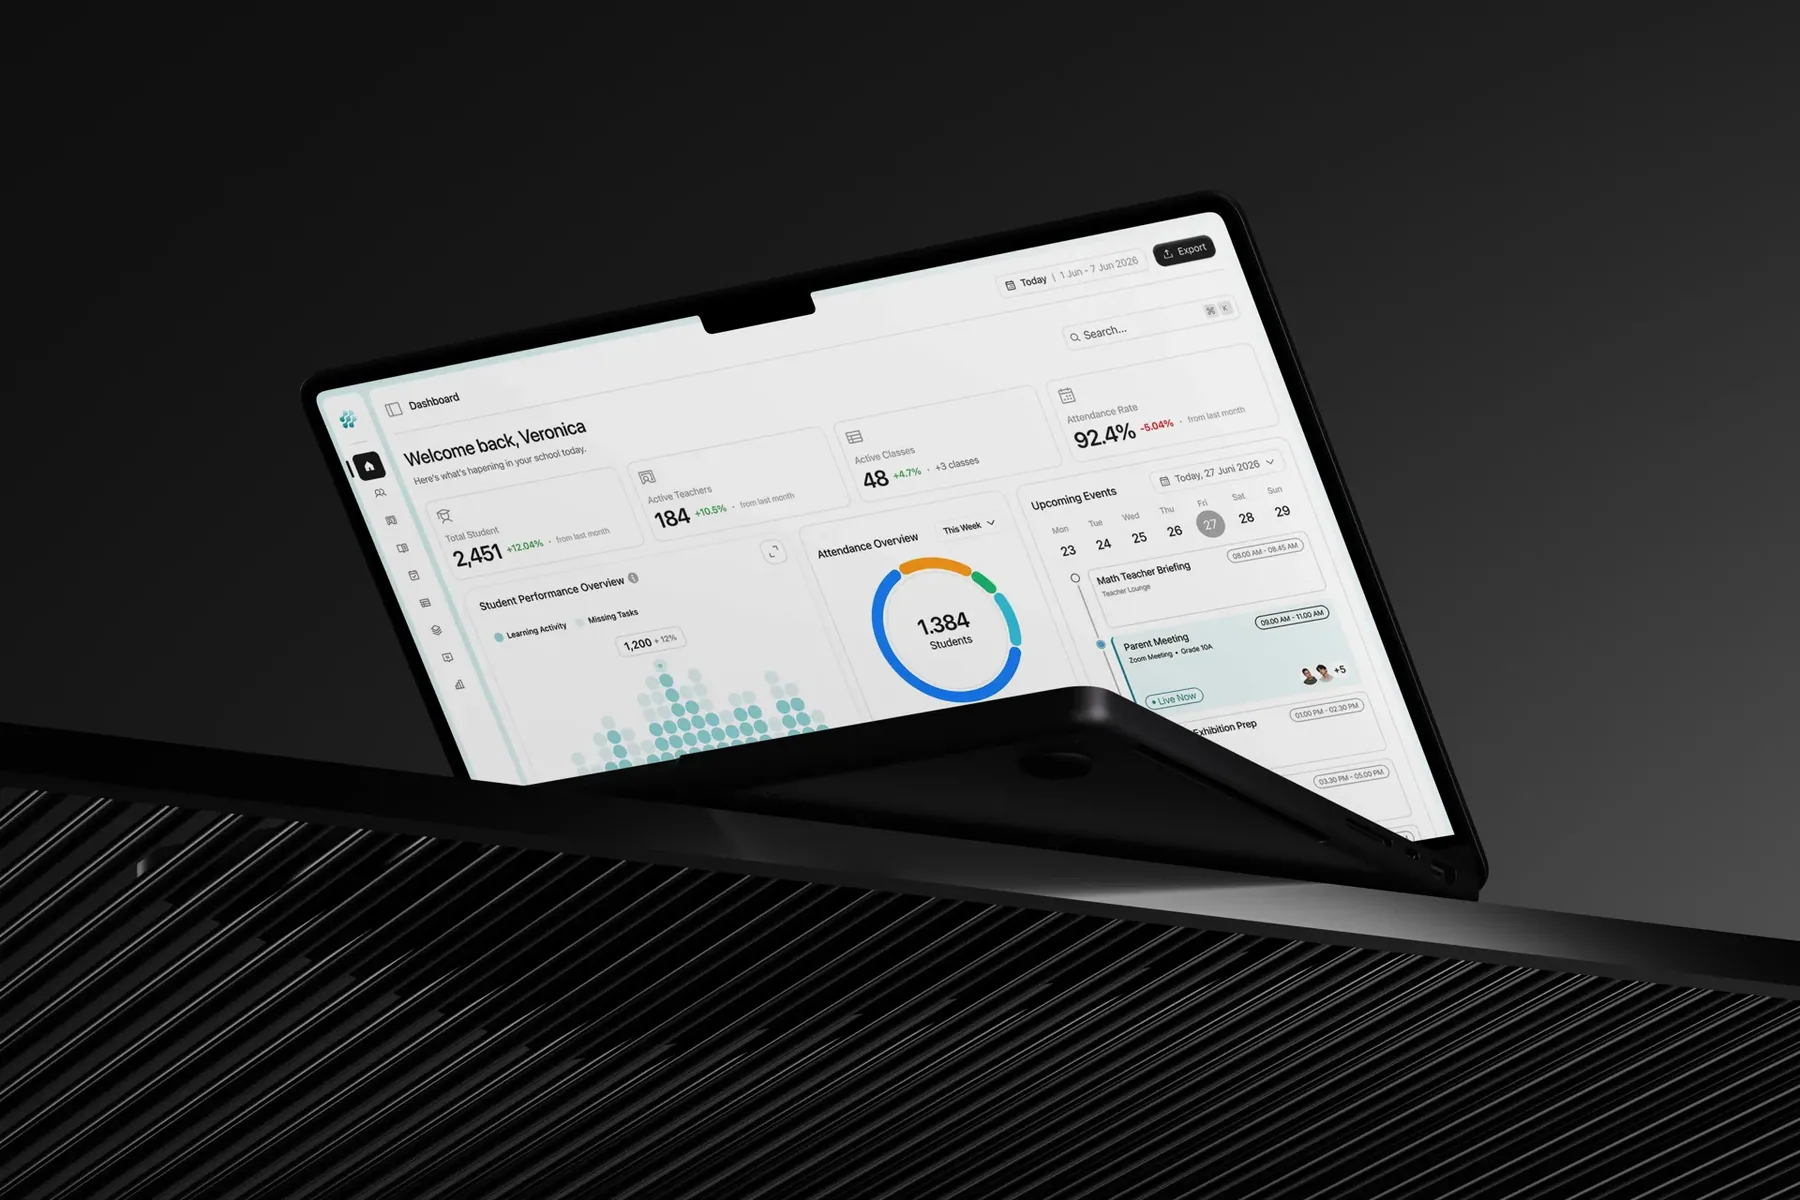 Design & web app
Victora: school management product design and web app.
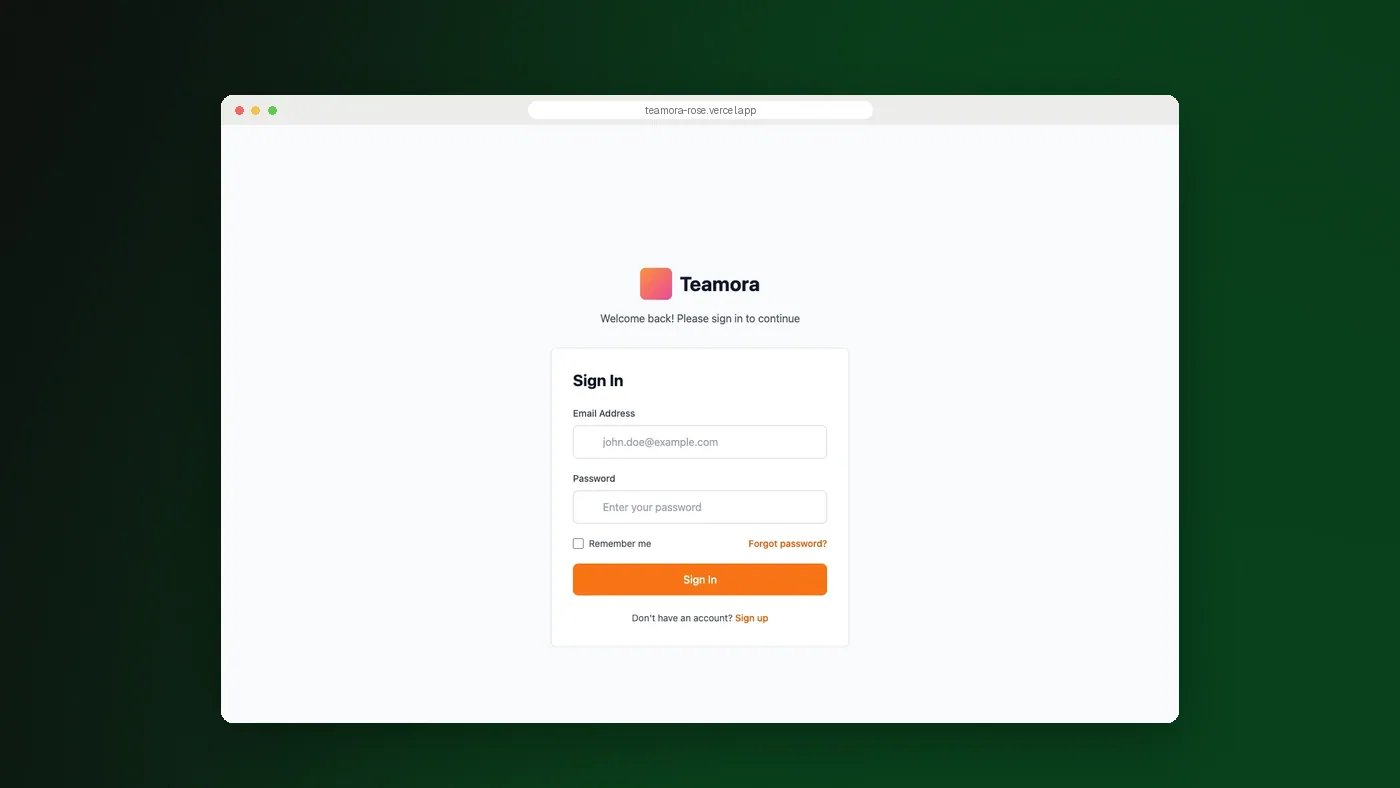 Design & web app
Teamora: a workspace for team collaboration.
Connected delivery
Security depends on the systems around it.
Controls need sound application design, clear data flows and named operational owners. Connect security work with the software it protects.
- Software & ProductBuild permissions, audit trails and reviewable workflows into the application brief, with clear boundaries for specialist security work.
- Data protectionDefine where sensitive data is held, how it moves and which users or systems can access it before selecting controls.
- Dedicated engineeringUse delivery capacity to address agreed application changes, document decisions and keep remediation work visible in the backlog.
- Cloud & APIsReview service identities, integration credentials and data flows alongside firewall and endpoint controls, not in isolation.
What determines the cost of security work?
The scope depends on assets, environments, users and the depth of assessment or implementation. An OEM deployment needs a view of the network, endpoints and operating requirements. VAPT needs an agreed asset list and testing boundaries. DLP and AML work need a clear view of data flows and existing processes. We define deliverables and dependencies before quoting; licensing, implementation and ongoing support should be distinguished rather than treated as one unspecified fee.
Which security service should we start with?
Start with the gap you need to address. Firewall or endpoint requirements point to Cybersecurity OEM solutions. Uncertainty about exposure points to VAPT. Sensitive information leaving approved channels points to DLP. Screening, monitoring and reporting workflows point to AML engineering. Scoping may reveal related work, but each service should have a defined purpose.
Can security work connect with software delivery?
Yes. Application changes may be needed to implement permissions, audit trails or remediation. Security requirements should be visible in the software brief, with clear acceptance criteria. A VAPT engagement remains separately authorised, and the assessment scope should identify which applications and environments are included.
Do you guarantee security or compliance?
No. Security controls and software can help an organisation meet and evidence obligations, but they do not remove risk or replace accountable ownership. Scope, configuration, operating procedures and ongoing review all matter. We keep the limits of each engagement explicit.
What is required before security testing starts?
Written authorisation, an agreed asset list and rules of engagement are required. Define exclusions, testing windows and escalation contacts. Social engineering and denial-of-service require explicit separate permission.
How is the security delivery schedule agreed?
The schedule follows the assets, access requirements, deployment dependencies and approval process. Testing windows must account for operational risk. For implementation work, agree configuration review, change approval and rollback responsibilities before setting the release date.
What evidence should an assessment provide?
Agree the report format in advance: scope, methods, findings, supporting evidence and remediation priorities. Retesting and closure evidence should be explicitly scoped.
Why connect security with governance engineering?
A control needs an owner and an operating process. Firewall rules need review, DLP alerts need handling and AML workflows need traceable decisions. Engineering should support those responsibilities with useful permissions, records and escalation paths, not imply that buying a tool completes the obligation.
What a regulator-ready VAPT report contains
7 min read
A useful assessment report makes scope, methods, evidence and remediation priorities clear. See what to agree before testing and how to track closure.
What the CBN's baseline standards for automated AML mean for your stack
5 min read
Review the engineering behind screening, transaction monitoring and reporting. Start with data flows, control ownership and evidence for compliance review.
Sophos or Fortinet? Choosing the security stack for a Nigerian enterprise
9 min read
Assess firewall and endpoint requirements against the network, existing controls and operating team. Product selection starts with the environment.
Designing internal tools people actually use
5 min read
Lessons from Relix CRM, Victora and Interoly: map the task, make system states visible and design around the context in which people work.
Software development as a service, or a fixed project? How to choose
4 min read
Compare ongoing engineering capacity with a defined project. Scope uncertainty, backlog ownership and integration dependencies shape the decision.
Other services
Connect security with the software it protects.
 Software & ProductApplications, interfaces, cloud and APIs built around your workflows.View category
 AML & compliance engineeringScreening, monitoring and reporting workflows with traceable decisions.View service
 All servicesSoftware, product design, cloud, security and governance from one team.View all