Choosing a security stack is an operating decision before it is a product decision. A branch network, a payment platform and a hospital with shared workstations have different constraints. Both Sophos and Fortinet offer network and endpoint security capabilities, but the right combination depends on coverage, configuration, licensing and the people available to respond.
Start with the estate, then compare Cybersecurity OEM solutions against a written set of requirements. Sparkr Digitals works with Sophos and Fortinet . For organisations in banking and financial services, the selection should also explain how logs, access controls and incident records will support review. The twelve criteria below are a procurement framework, not a claim that one vendor wins every workload or that any appliance guarantees compliance.
How to use these twelve decision criteria
Build an asset and traffic inventory before requesting prices. Record branch links, remote users, supported operating systems, identity providers and the services that cannot tolerate disruption. Then require each proposal to name the products, subscriptions, deployment model and exclusions. Compare equivalent controls, not a firewall-only quote against a bundle containing endpoint protection and managed response.
The descriptions here follow the vendor references in our research. Product names do not establish entitlement: confirm current features, supported versions and regional availability in the written quotation before purchase.
Define the estate, endpoint cover and response model
These first three criteria establish what is protected and who acts when a control detects something suspicious.
1. Estate size and throughput
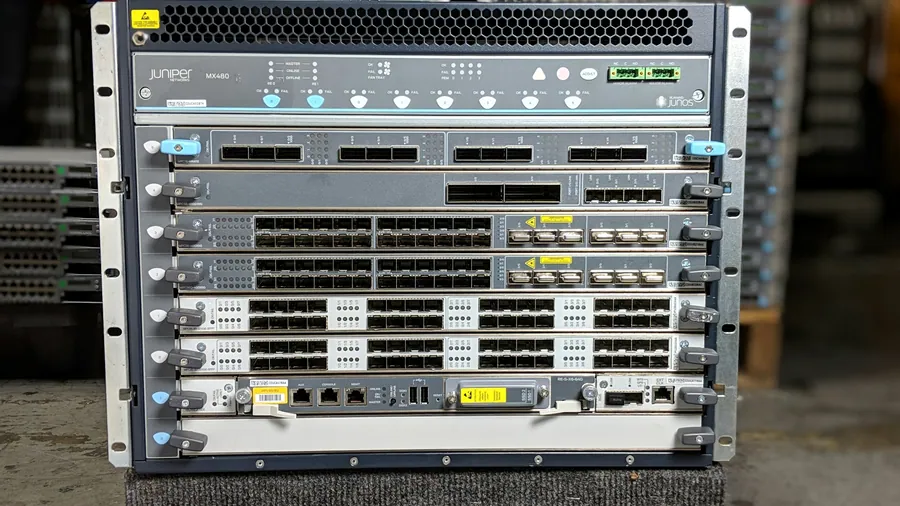
Sophos Firewall and FortiGate both belong on a network-security shortlist. Size for concurrent sessions, encrypted traffic, branch links and the inspection features you will enable. Appliance headline throughput is not a promise for your workload. Test a representative policy and traffic mix, including failover where required. Require a scoped pilot: record traffic assumptions, enabled controls and acceptance criteria before selecting appliance models.
2. Endpoint coverage
Sophos Endpoint and FortiEDR address endpoint security. Sophos Endpoint covers malware, exploit and ransomware protection with EDR/XDR options; FortiEDR provides prevention, detection, investigation and response capabilities. Verify operating-system support, server coverage, exclusions and agent compatibility against the actual fleet. Check every device class: include shared workstations, servers and remote laptops rather than counting only office desktops.
3. Managed detection and response
Sophos MDR provides expert-led, 24/7 managed detection, investigation and response. A Fortinet-based proposal must separately name the people or service responsible for those activities. Compare authorised actions, escalation, telemetry coverage and incident handover. Do not equate an endpoint product or a detection dashboard with a staffed response service. Name the responder: confirm who can isolate a device, who approves action and who stays accountable after escalation.
Compare access, administration and reporting needs
A product demonstration should use your identity flows, operator roles and reporting questions rather than a generic dashboard tour.
4. SASE and ZTNA
Sophos ZTNA supports identity- and policy-controlled application access; FortiSASE provides cloud-delivered secure access including SWG, ZTNA and CASB. They are not identical bundles. Compare private-application access, internet controls, identity integration and user locations. Validate the precise FortiClient role and entitlements in the proposed design. Test real access paths: verify both permitted and denied access using your applications, identities and remote-user conditions.
5. Central management
Sophos Central provides cloud management for Sophos products; Fortinet Security Fabric is an integration architecture, not simply an equivalent console. Ask the Fortinet proposal to name its management components. In both designs, test administrator roles, MFA, policy approval, configuration recovery and branch administration. Confirm platform branding and entitlements in the quotation. Demonstrate the workflow: ask an administrator to change policy, obtain approval and recover the previous configuration.
6. Logging and reporting
Sophos reporting should be compared with a fully specified FortiAnalyzer design where proposed. FortiAnalyzer provides central logging, analytics and reporting. For both stacks, verify log sources, retention, storage, export and administrator access. A useful dashboard does not by itself establish a complete, durable audit trail. Request a sample record: trace a policy change and a security event from source log to investigation notes and retained evidence.
Test commercial terms and day-to-day operability
Renewals, escalation paths and administrator skills matter throughout the contract. Treat them as requirements, not details to settle after installation.
7. Licensing and renewals
Sophos licensing and Fortinet licensing need itemised comparisons. Name every product, subscription, device or user quantity, term and support entitlement. Document expiry behaviour, renewal dates and growth assumptions. Separate required controls from optional features, and confirm what remains available if a subscription lapses. Compare equivalent scope: do not compare a bare appliance quotation with a proposal containing endpoint protection, reporting and managed response.
8. Local support
Sophos support and Fortinet support should be assessed through the actual contracted escalation path. Confirm support hours, contacts, remote access arrangements and hardware replacement terms for your locations. Local availability and response promises must be written into the offer, not inferred from a vendor logo. Test the handover: identify who opens a vendor case, who updates your team and who owns a replacement or workaround.
9. Skills and operational fit
Sophos administration and Fortinet administration both require trained operators and controlled change. Pilot common tasks: onboarding a device, investigating an alert, adjusting firewall policy and restoring configuration. Record the training and documentation required. Familiarity can reduce transition effort, but it should not override a material coverage gap. Assess the real team: ask the people who will operate the stack to complete the pilot tasks and identify support needs.
Check integration, evidence and whole-life cost
The final criteria test whether the proposed stack fits the rest of the organisation and can produce useful evidence throughout its service life. This matters especially in healthcare environments: shared devices and clinical applications need controls that staff can operate without weakening access boundaries.
10. Integration with existing tools
Sophos MDR integrations can incorporate existing security tools, while Fortinet Security Fabric links network, endpoint and cloud controls for coordinated visibility and response. Verify the actual integration, data direction, permissions, connector support and licence. A published integration name is not proof that your deployed versions support the required action. Prove the data path: send a representative event, verify its fields and confirm the approved response reaches the intended control.
11. Compliance evidence
Sophos control records and Fortinet control records should be evaluated against your obligations. Require access reviews, policy-change trails, incident records and remediation evidence in an accessible format. Buying a stack does not establish compliance; owners must configure, operate and review it. Map obligations to evidence: document which records come from the stack and which must come from your wider Security & Governance programme, with accountable owners for both.
12. Total cost of ownership
Sophos whole-life cost should be compared with Fortinet whole-life cost over the same planning period and scope. Include subscriptions, hosting, logging, support, training, migration, administrator effort and exit costs. Document currency, tax and renewal assumptions rather than claiming a fixed saving from brand choice. Approve the full commitment: retain the assumptions, exclusions and operational responsibilities alongside the final price.
What a defensible selection has in common
A useful comparison ends with a decision record rather than a brand preference. These four habits make the reasoning inspectable when the estate grows, the team changes or a renewal arrives.
- Requirements have acceptance tests: prove supported devices, access paths and reporting outputs against the agreed scope, not a brochure summary.
- Every control has an operator: name who reviews alerts, approves policy changes, handles escalation and checks whether fixes worked.
- Every entitlement is explicit: record products, subscriptions, support hours and exclusions alongside the renewal and expiry dates.
- Evidence is designed into operations: keep approved policy changes, access reviews and investigation records. For the reporting discipline, see what a regulator-ready VAPT report contains.
Neither vendor should be selected solely because it appears to simplify procurement. A consolidated stack can reduce some handovers while creating concentration and migration risks. Our Cybersecurity OEM solutions work should begin with agreed scope and acceptance criteria. Prefer the combination that fits your estate, gives your team a workable response process and makes the total commitment clear. Retain the comparison, unresolved gaps and formal risk acceptance as part of the decision record.
A practical caveat: a successful pilot does not remove operational risk. Recheck policy, identity, logging and escalation after deployment and material changes. Evidence also has to support time-sensitive decisions, as discussed in the NDPA and GAID breach-notification clock.
The checklist to run before approving your stack
- Both proposals cover the same assets, users and required security controls.
- The pilot exercises representative traffic with intended inspection enabled.
- Endpoint support, exclusions and response ownership are documented.
- Logs, retention and reporting outputs meet your review needs.
- Renewals, support escalation and replacement terms are in writing.
- Migration, rollback, training and exit costs are included in the decision.
Choose on tested fit and accountable operation, not a universal winner. Our Cybersecurity OEM solutions service can help frame the comparison around your estate and obligations. To review scope, acceptance criteria and the assumptions behind a quotation, talk to us.