Payment flows need more than a polished checkout. Make every ledger entry and exception traceable.
Payment software built for traceable transactions and recovery

Why it matters
Payment teams must evidence identity checks, transaction monitoring and reconciliation to regulators and sponsor banks. Resilient flows need traceable ledger changes and tested recovery, not just a convincing onboarding demo.
The problem
A polished interface is not proof of operational control.
Where payment flows lose control
Payment teams must evidence identity checks, transaction monitoring and reconciliation to regulators and sponsor banks. Resilient flows need traceable ledger changes and tested recovery, not just a convincing onboarding demo.
The traps
Trap 0101 / 04
Retries without control
Duplicate debits
Retries repeat a debit when an upstream response arrives late. Define idempotency and recovery paths.
Trap 0202 / 04
States without owners
Unresolved payments
Pending payments sit between the gateway and ledger. Assign exception queues and reconciliation owners.
Trap 0303 / 04
Privileges accumulate
Unchecked access
Staff retain payment and refund permissions after roles change. Review access and approval boundaries.
Trap 0404 / 04
Signals without action
Unusable alerts
Monitoring produces alerts without case history or disposition. Keep decisions and evidence together.
Fintech & Payments, in figures
Nigerian NIP volumes show the scale reconciliation and recovery must support. The value is NIBSS data reported by Lagos Post; the growth covers 2022–2024. These figures describe the market, not Sparkr project results.
Annual NIP transactions
≈11bn
Nearly eleven billion Nigerian NIP transactions in 2024; NIBSS, published February 2026.
NIP transfer value
₦1.07qd
2024 Nigerian NIP value; NIBSS data reported by Lagos Post, January 2025.
NIP volume growth
120%
Growth in Nigerian NIP volume, 2022–2024; CBN report cited by NIBSS, February 2026.
Breach notification
72h
Notify NDPC within 72 hours of awareness where a breach risks individuals' rights or freedoms; NDPA 2023 / GAID 2025.
Sources: NIBSS: NIP transactions, 2024; Lagos Post: NIBSS payment value, 2024; NIBSS: NIP volume growth, 2022–2024; NDPC, NDPA 2023 / GAID 2025 (72-hour risk-based notification).
04
Public sources behind the figures on this page
- 01NIBSS: NIP transactions, 2024
- 02Lagos Post: NIBSS payment value, 2024
- 03NIBSS: NIP volume growth, 2022–2024
- 04NDPC: GAID 2025 and breach notification
Figures retain their source periods and scope. They describe sector conditions and legal duties, not Sparkr project outcomes.
How we work with your team
Start with the workflow, then test the controls
We map payment states, ledger entries and sponsor-bank dependencies. Together we agree owners, acceptance criteria and the evidence needed before delivery starts.
Step 01
Scope & Discovery
We map critical tasks, system boundaries and risk with your delivery and operational owners.
Step 02
Architecture & Controls
We define access rules, data flows and failure handling before implementation decisions are fixed.
Step 03
Workflow Design
We prototype critical tasks and review them with users before building the full workflow.
Step 04
Build & Test
We implement in reviewed increments, testing permissions, integrations and exception handling.
Step 05
Release & Operational Handover
We agree release checks, recovery procedures and support ownership, then hand over evidence.
Selected work
Related work and delivery capabilities
- Operational workflows
- Access reviews
- Reconciliation
- Audit evidence
- Recovery planning
Services
The services we bring to this sector.
 AML & compliance engineeringMonitoring, case workflows and reporting evidence.View service
 Cloud & API engineeringConnect systems with tested failure and recovery paths.View service
 Custom software developmentOperational tools with clear ownership and audit trails.View service
 VAPT & threat assessmentsAuthorised testing, actionable findings and retesting.View service
How do you scope fintech & payments work?
We start with the workflow, system boundaries and the evidence your team needs. The scope records users, integrations, data categories, access roles, operational risks and acceptance criteria. We then agree delivery phases and commercial terms. We do not publish a fixed price before reviewing complexity, dependencies, migration needs and the controls that must be tested.
Can you work with our existing systems?
We review available APIs, data ownership and integration constraints before proposing changes. The plan includes failure handling, reconciliation where relevant and a staged release. We agree what stays, what changes and who owns each dependency rather than assuming a full replacement is necessary.
How do you protect sensitive records?
We define role-based access, encryption needs, data handling rules and audit trails with your owners. Test environments should use appropriate masked or synthetic data. Retention, exports and privileged access need explicit decisions, not default permissions.
Which financial rules guide the control design?
We confirm the licence and activity first. CBN AML/CFT/CPF Regulations 2022 inform monitoring and reporting controls. The May 2024 cybersecurity framework applies to DMBs and PSBs, not every PSP. Applicable duties are confirmed with your compliance team before implementation.
How do you agree delivery timescales?
Timescales follow scope, integration access, data quality and review availability. We agree milestones after discovery, with clear acceptance criteria and dependency owners. A staged release can prioritise essential workflows without hiding unfinished controls.
What related work can we review?
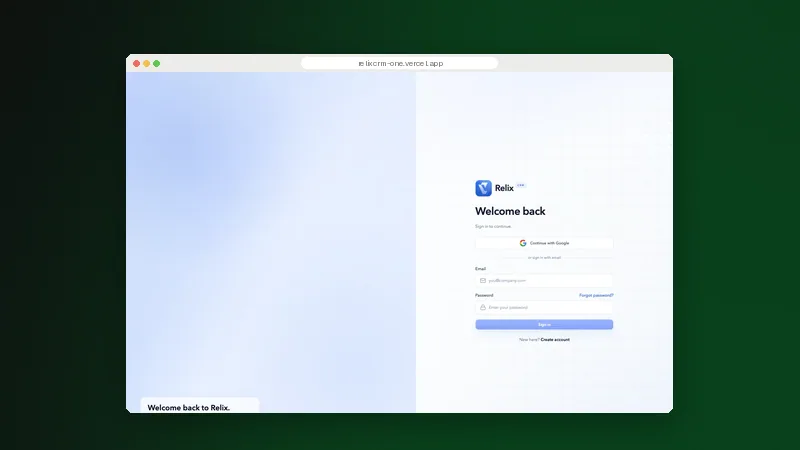
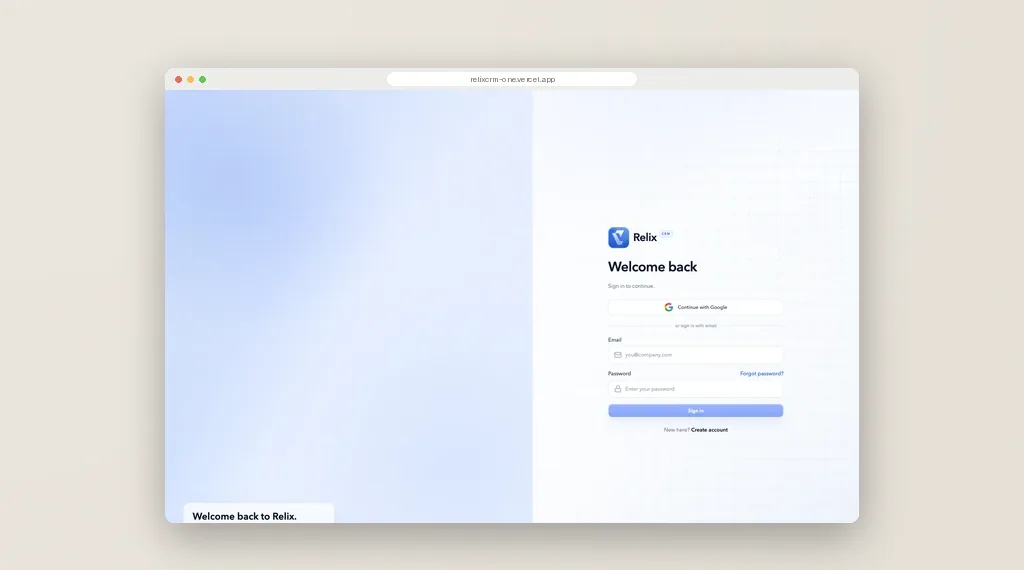
Systhems is an independent cybersecurity website concept, not a banking deployment. Relix CRM demonstrates leads, deals and invoicing workflows; its workspace requires an account. These are relevant design references, not evidence of payment-processing results.
Sophos or Fortinet? Choosing the security stack for a Nigerian enterprise
7 min read
Compare deployment needs, management workflows and response ownership before choosing a security stack. Product scope and licensing matter as much as the appliance specification.
Software development as a service, or a fixed project? How to choose
5 min read
A continuing backlog and a fixed delivery scope need different commercial arrangements. Compare ownership, acceptance criteria and engineering cadence before deciding how to engage.
Sophos or Fortinet? Choosing the security stack for a Nigerian enterprise
7 min read
Compare deployment needs, management workflows and response ownership before choosing a security stack. Product scope and licensing matter as much as the appliance specification.
What a regulator-ready VAPT report contains
6 min read
Written authorisation, scope, reproducible findings and retest evidence make a security assessment useful. See what risk teams need beyond an automated list of vulnerabilities.
What the CBN's baseline standards for automated AML mean for your stack
7 min read
The final 10 March 2026 standards set different implementation windows for DMBs and OFIs. Review monitoring, case management, integrations and the evidence your roadmap needs.
Other industries
Back to all industries