01
Technical leadership in the room
Official OEM Partners: Sophos & Fortinet
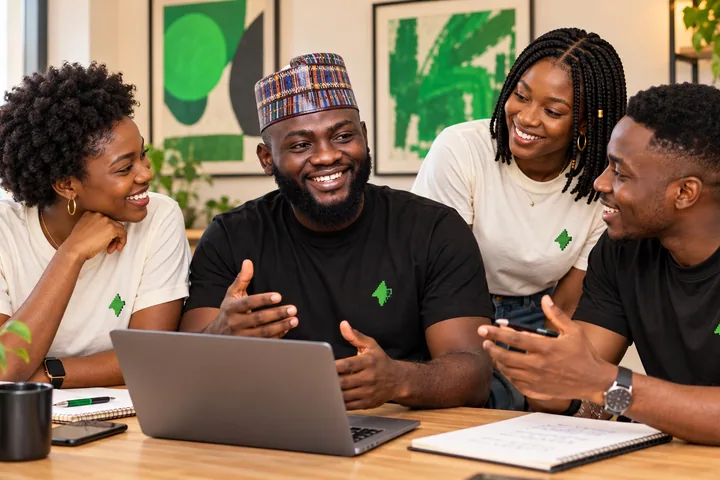
Quadri Ismail, our Chief Technical Officer, anchors architecture, engineering and security delivery. Technical decisions stay connected to the work.

 Contact
Relix CRM · sales operations
Sophos & Fortinet OEM partner
Software development as a service
Custom software development
Product design & UX
Cloud & API engineering
Cybersecurity OEM solutions
VAPT & threat assessments
Data loss prevention (DLP)
AML & compliance engineering
Banking & Finance
Healthcare
Commerce & Logistics
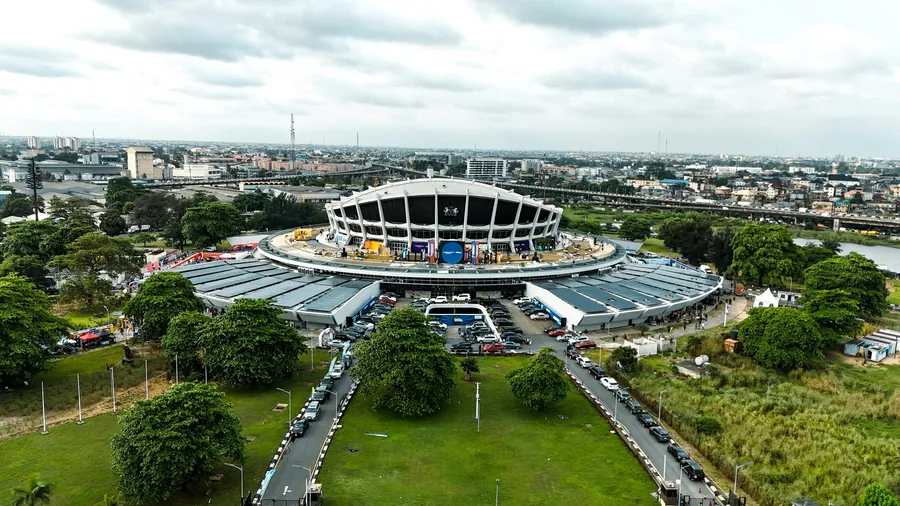
Public Sector
Education
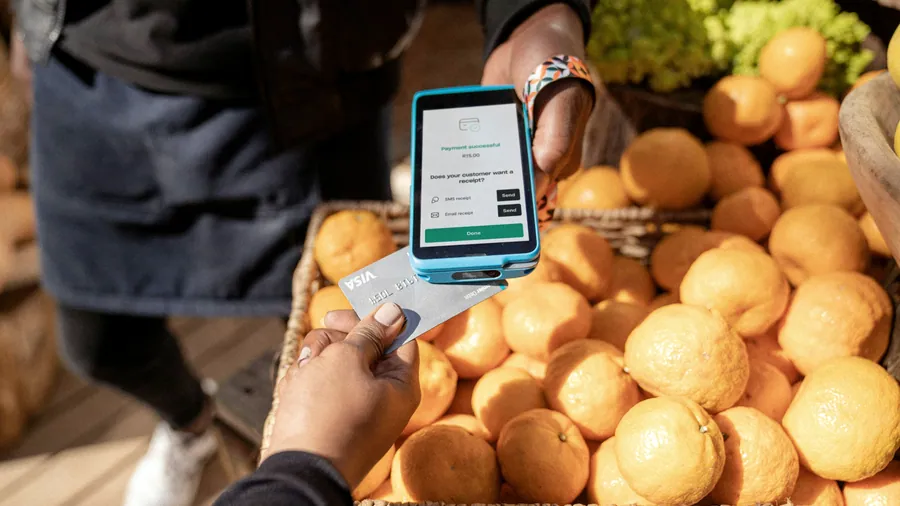
Fintech & Payments
ORGANISATIONS WE HAVE WORKED WITH
From public institutions to fintechs and growing businesses, these organisations have worked with Sparkr Digitals. Our focus: software shaped around the people and processes it serves.
Your software must serve the business and withstand scrutiny. We connect product engineering, security and governance from the start.
Our services
Explore our two pillars and the capabilities within them: product engineering, security controls and evidence for oversight.
Service 01
Platforms, internal tools and integrations built around your workflows. From product design to delivery, we connect what people need with how systems work.
Service 02
Identity & RBAC / DLP & Encryption / VAPT Audits / AML Compliance / Sophos & Fortinet OEM
Service 03
Protect sensitive records with data controls, encryption and clear access policies.
Service 04
Dedicated engineering capacity, managed delivery and continuous product enhancement.
Service 05
Connect systems through APIs. Plan cloud infrastructure around capacity, recovery and operational ownership.
Selected work
Explore our own product work and interface concepts, from a cybersecurity website direction to clinical, sales, school and team workspaces. Each case study states its scope and access limits.


Clinical interface design and prototype; the demo opens at sign-in, not in a live care setting.

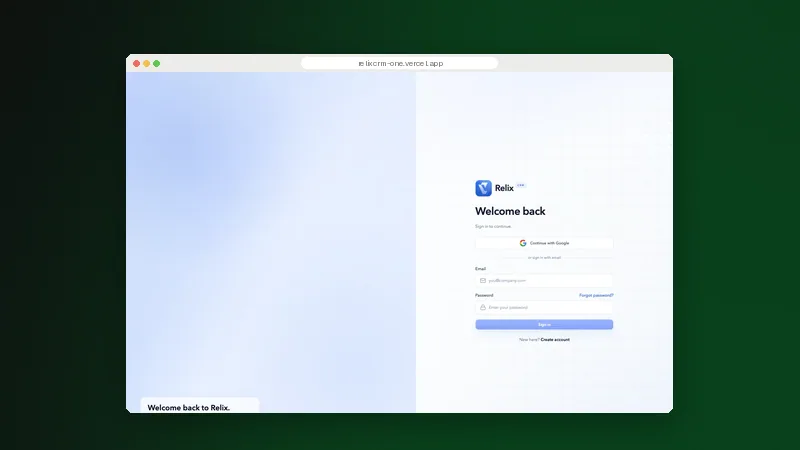
Product design and web app; workspace access needs an account.

School management product design and web app; the demo opens at sign-in.

( Our approach )
A ledger, a patient record or an access review carries obligations beyond the screen. We start with the workflow and its risks.
Sparkr Digitals brings software and product engineering together with security and governance. Based in Lagos, we work with organisations across Nigeria and beyond. We make requirements, handoffs and control decisions explicit, so business, technology and risk teams can assess the same plan.
Why work with us
Good delivery makes decisions visible. We connect product needs, technical constraints and control requirements in one plan. Your team should know what is being built, who owns each decision and what evidence will support review.
01
Official OEM Partners: Sophos & Fortinet
Quadri Ismail, our Chief Technical Officer, anchors architecture, engineering and security delivery. Technical decisions stay connected to the work.
02
Scope, dependencies and acceptance criteria.
We define the workflow, integration boundaries and delivery stages before implementation. Reviews focus on what the software must do and how the team will verify it.

03
Permissions and evidence, not afterthoughts.
We plan access roles, sensitive-data handling and audit trails alongside the user journey, rather than leaving them until release.

04
Product operations stay close to the work.
Amarachi Nwosu, our Chief Operating Officer, anchors delivery and product operations. We keep business priorities connected to implementation decisions.

Industries
From reconciliation to ward rounds and admissions season, we shape software and security around the records, decisions and controls your teams depend on.
A modern banking interface cannot compensate for weak authorisation. Prioritise privileged access, reconciliation and evidence for internal audit.
Disconnected patient records create uncertainty at handover. Plan identity, confidentiality and continuity alongside clinical workflows.
Stock records drift when receiving, dispatch and returns sit in separate tools. Connect each movement to an accountable record.
A public portal is not an end-to-end service if citizens still chase paper approvals. Define ownership, access and auditable decisions.
Admissions, fees and attendance need clear permissions and reliable records. Design for the school office as well as the classroom.
A polished checkout can hide unresolved payments. Plan traceable ledger changes, duplicate handling and reconciliation before launch.
7 min read
Review the 10 March 2026 standards through the systems they affect: transaction monitoring, investigation workflows, reporting and implementation planning.
6 min read
Prepare for breach assessment, escalation and notification. Map the records, responsibilities and evidence your team needs when personal data may be at risk.
7 min read
Written authorisation, scope, reproducible findings and remediation evidence: what a useful assessment report should let technical and oversight teams verify.
8 min read
Compare firewall, endpoint and management requirements before choosing a stack. Start with your estate, operational capacity and control priorities.
5 min read
Choose the delivery model around scope certainty, engineering capacity and product ownership. A practical way to compare ongoing development with a defined project.
6 min read
Lessons from Relix CRM, Victora and Interoly: organise screens around tasks, preserve context across handoffs and test the workflow before claiming improvement.
How we work
Sparkr Digitals works with regulated and ambitious organisations: teams building platforms, managing sensitive records and answering to customers, boards and regulators.
We connect the work of engineering and risk teams, so product decisions account for controls, delivery and operational ownership.
Useful software starts with an understood workflow. Responsible delivery makes its assumptions visible. Our priorities are clarity, accountability and evidence.
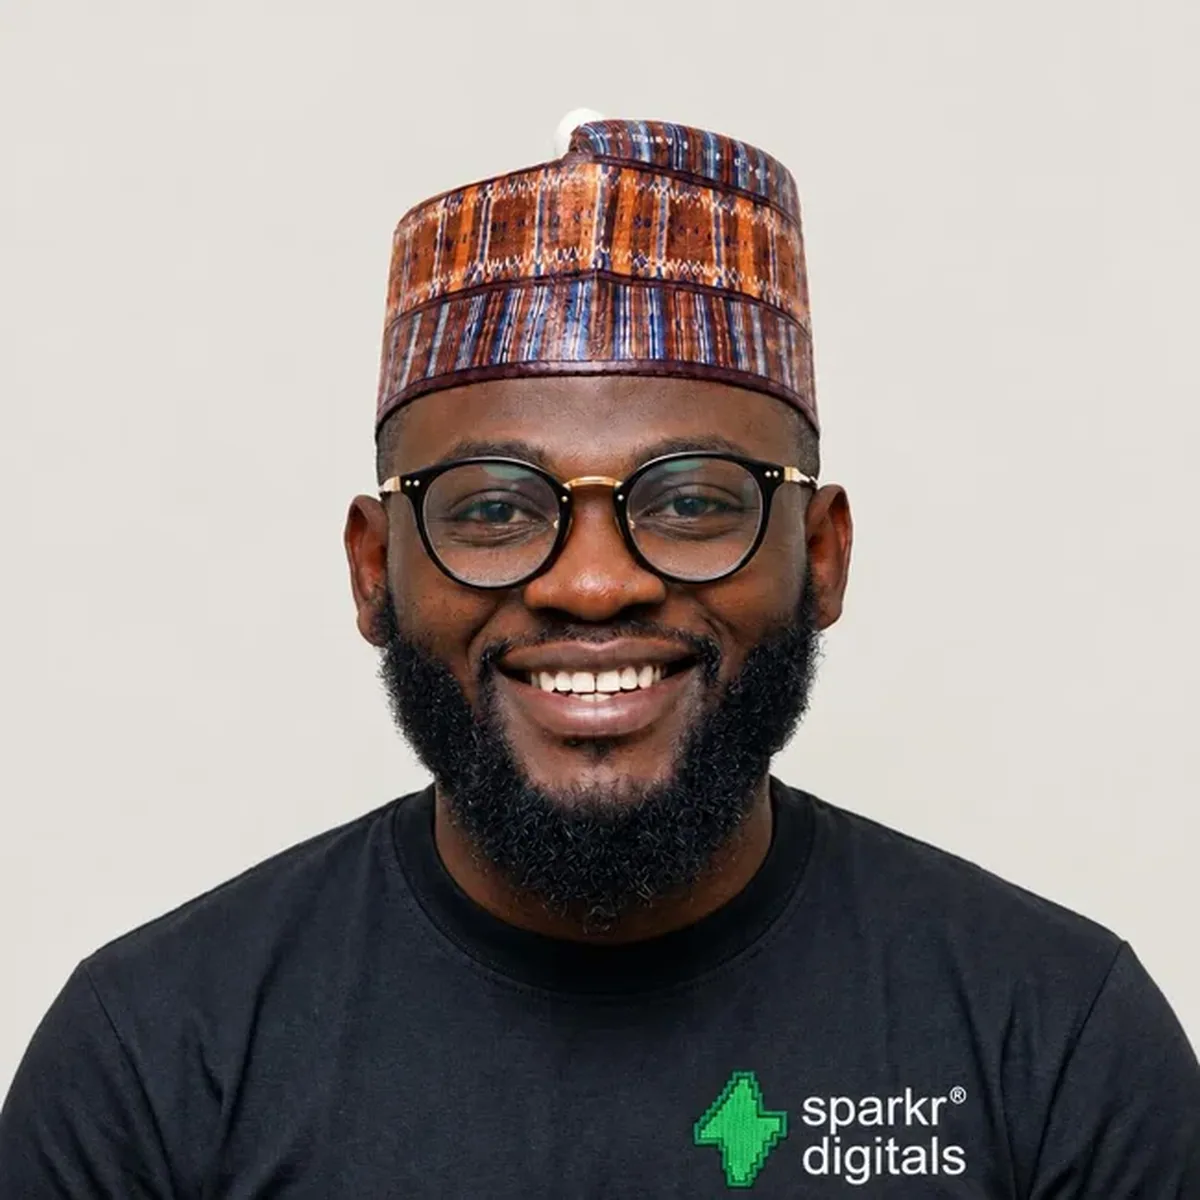 Quadri IsmailChief Technical Officer
Meet the team“We agree system boundaries, access roles and integration ownership before a line of code is written. A plan should expose its assumptions, so your engineers and auditors can challenge them early.”
 Amarachi NwosuChief Operating Officer
Meet the team“We start with the task and the handoff. Every record needs a clear context, and every proposed workflow is tested with the people who will run it before we call it finished.”
 Adebowale Samson AdegbiteChief Executive Manager
Meet the team“Delivery includes the decisions that keep software useful after release: who administers it, who reviews permissions and who responds when something goes wrong.”
 Sparkr DigitalsSecurity & Governance practice
Explore Security & Governance“Controls only count when they leave evidence. We plan audit trails, assessment scope and remediation records alongside the systems they protect.”
Let's keep in touch
Get in touchSparkr Digitals builds software and helps organisations secure it. Our two pillars are Software & Product and Security & Governance. We design and build platforms, internal tools, web and mobile applications, cloud services and APIs. Security work covers OEM solutions, VAPT, data loss prevention and AML & compliance engineering. We work with regulated and ambitious organisations, connecting operational workflows with access controls, sensitive-data handling and evidence for review.
Pricing depends on the scope, system boundaries and delivery model. A defined application, ongoing engineering capacity and a security assessment need different plans. We first clarify workflows, integrations, data sensitivity, environments and acceptance criteria. The proposal should make deliverables, dependencies and responsibilities explicit. Where work needs phasing, we agree which operational needs and risks to address first. We do not publish a fixed price before understanding those requirements.
Timing depends on scope, integrations, data migration and the reviews your organisation needs. We agree delivery stages and acceptance criteria during planning. A focused prototype and a production platform require different levels of testing, security review and operational preparation. We establish the schedule around those requirements rather than a generic launch promise.
Operational ownership is part of planning. We discuss who will administer accounts, approve access, maintain records and handle changes. Those responsibilities inform permissions, interfaces and handover requirements. Support and maintenance needs should be agreed in the scope, so your team understands what it owns after release and where further engineering input is needed.
We start with the workflow, existing systems and operational constraints. Integration requirements, data sensitivity, expected load and your internal capabilities guide architecture choices. We consider how the platform will be tested, deployed, monitored and maintained, not just how quickly a first screen can be built. Cloud & API engineering connects the new software to the systems it must work with. The technical plan should make trade-offs and ownership clear.
Security & Governance covers Cybersecurity OEM solutions, VAPT & threat assessments, Data loss prevention (DLP), and AML & compliance engineering. We are Official OEM Partners: Sophos & Fortinet. Our work helps organisations assess exposure, apply controls and evidence obligations. It does not guarantee security or compliance. Testing requires written authorisation, with social engineering and denial-of-service work subject to explicit separate permission.
We begin with the business workflow, the people using it and the systems it touches. We then clarify scope, dependencies, security requirements and acceptance criteria. Design makes assumptions visible before implementation; engineering turns the agreed direction into working software. Testing and review check the result against the agreed requirements. Delivery planning also covers release, handover and operational ownership, with support needs agreed for the engagement.
Software decisions affect access, data handling and the evidence available to an auditor. Treating security as a separate final check can leave those decisions unresolved. Sparkr Digitals connects product design, architecture and engineering with security and governance requirements. That means discussing permissions, audit trails, integrations and operational responsibilities while the platform is taking shape. Our case studies distinguish prototypes and design work from production use and measured outcomes.
Sparkr Digitals is based in Lagos, Nigeria. We work with organisations across Nigeria and beyond, including regulated institutions and ambitious businesses. Contact hello@sparkrdigitals.com to discuss your requirements.


