Your risk committee needs evidence. Build controls that hold across core systems, channels and vendors.
Banking systems built for control, resilience and audit evidence

Why it matters
Banks must show supervisors, internal audit and risk committees how privileged access, transaction integrity and incident response are controlled. Core integrations, vendor oversight and recovery procedures need evidence that can be tested.
The problem
Core systems need control, not just a new interface.
Where banking systems leave risk exposed
Banks must show supervisors, internal audit and risk committees how privileged access, transaction integrity and incident response are controlled. Core integrations, vendor oversight and recovery procedures need evidence that can be tested.
The traps
Trap 0101 / 04
A modern interface
Weak authorisation
New screens leave old privilege paths intact. Test approval rules across channels and core integrations.
Trap 0202 / 04
Hidden dependencies
Fragile core links
A core-system timeout becomes a customer outage. Define failure handling and rehearse recovery.
Trap 0303 / 04
Risk outside the bank
Unreviewed vendors
Supplier access and data flows escape routine review. Record owners, permissions and exit arrangements.
Trap 0404 / 04
Controls without records
Missing evidence
Teams describe a control but cannot produce its history. Retain logs, access reviews and test evidence.
Banking & Financial Services, in figures
NIBSS reports fraud across Nigeria's financial ecosystem, not commercial banks alone. The lower 2025 loss total does not remove the need for tested access controls, transaction integrity and response procedures.
Annual fraud losses
₦25.85bn
2025 digital-payment fraud losses across Nigeria's financial ecosystem, not banks alone.
Prior-year fraud losses
₦52.26bn
2024 fraud losses across Nigeria's financial ecosystem; NIBSS comparison published January 2026.
Reported fraud incidents
67,518
Fraud incidents in Nigeria's financial ecosystem in 2025; NIBSS, January 2026.
Breach notification
72h
Notify NDPC within 72 hours of awareness where a breach risks individuals' rights or freedoms; NDPA 2023 / GAID 2025.
Sources: NIBSS: digital-payment fraud, 2025; NIBSS: digital-payment fraud, 2024 comparison; NIBSS: reported fraud incidents, 2025; NDPC, NDPA 2023 / GAID 2025 (72-hour risk-based notification).
03
Public sources behind the figures on this page
- 01NIBSS: digital-payment fraud, 2025
- 02NIBSS: digital-payment fraud, 2024 comparison and related sector figures
- 03NDPC: GAID 2025 and breach notification
Figures retain their source periods and scope. They describe sector conditions and legal duties, not Sparkr project outcomes.
How we work with your team
Start with the workflow, then test the controls
We map core integrations, privileged access and recovery dependencies. Together we agree owners, acceptance criteria and the evidence needed before delivery starts.
Step 01
Scope & Discovery
We map critical tasks, system boundaries and risk with your delivery and operational owners.
Step 02
Architecture & Controls
We define access rules, data flows and failure handling before implementation decisions are fixed.
Step 03
Workflow Design
We prototype critical tasks and review them with users before building the full workflow.
Step 04
Build & Test
We implement in reviewed increments, testing permissions, integrations and exception handling.
Step 05
Release & Operational Handover
We agree release checks, recovery procedures and support ownership, then hand over evidence.
Selected work
Related work and delivery capabilities
Independent cybersecurity website concept: brand direction, UX/UI and design system.
Monitoring, case workflows and reporting evidence.
Authorised testing, actionable findings and retesting.
Connect systems with tested failure and recovery paths.
- Operational workflows
- Access reviews
- Reconciliation
- Audit evidence
- Recovery planning
Services
The services we bring to this sector.
 Data loss prevention (DLP)Control sensitive data across access, sharing and exports.View service
 VAPT & threat assessmentsAuthorised testing, actionable findings and retesting.View service
 Custom software developmentOperational tools with clear ownership and audit trails.View service
 AML & compliance engineeringMonitoring, case workflows and reporting evidence.View service
How do you scope banking & financial services work?
We start with the workflow, system boundaries and the evidence your team needs. The scope records users, integrations, data categories, access roles, operational risks and acceptance criteria. We then agree delivery phases and commercial terms. We do not publish a fixed price before reviewing complexity, dependencies, migration needs and the controls that must be tested.
Can you work with our existing systems?
We review available APIs, data ownership and integration constraints before proposing changes. The plan includes failure handling, reconciliation where relevant and a staged release. We agree what stays, what changes and who owns each dependency rather than assuming a full replacement is necessary.
How do you protect sensitive records?
We define role-based access, encryption needs, data handling rules and audit trails with your owners. Test environments should use appropriate masked or synthetic data. Retention, exports and privileged access need explicit decisions, not default permissions.
How do the final CBN AML standards affect scope?
The final standards were issued on 10 March 2026. DMBs have 18 months and OFIs 24 months for full compliance, with roadmaps due within three months. We scope monitoring, case management, integrations and audit evidence with your compliance team; we do not promise regulatory approval.
How do you agree delivery timescales?
Timescales follow scope, integration access, data quality and review availability. We agree milestones after discovery, with clear acceptance criteria and dependency owners. A staged release can prioritise essential workflows without hiding unfinished controls.
What related work can we review?
Systhems is an independent cybersecurity website concept, not evidence of deployed bank security controls. For banking delivery we agree the technical scope, authorisation, acceptance criteria and evidence separately.
What the CBN's baseline standards for automated AML mean for your stack
7 min read
The final 10 March 2026 standards set different implementation windows for DMBs and OFIs. Review monitoring, case management, integrations and the evidence your roadmap needs.
What a regulator-ready VAPT report contains
6 min read
Written authorisation, scope, reproducible findings and retest evidence make a security assessment useful. See what risk teams need beyond an automated list of vulnerabilities.
Designing internal tools people actually use
5 min read
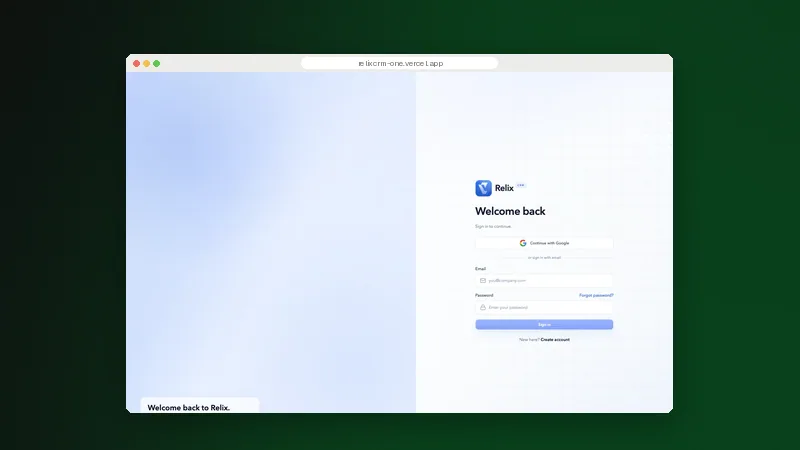
Relix CRM, Victora and Interoly show different contexts for operational work. Start with real tasks, information hierarchy and reviewable decisions rather than adding another dashboard.
Software development as a service, or a fixed project? How to choose
5 min read
A continuing backlog and a fixed delivery scope need different commercial arrangements. Compare ownership, acceptance criteria and engineering cadence before deciding how to engage.
The 72-hour clock: what NDPA and the GAID demand of your systems
6 min read
Notification depends on risk to individuals, not simply an incident label. Prepare the access logs, incident ownership and assessment records needed to act within the statutory window.
Other industries
Back to all industries