Clinicians need the right patient context. Protect records while making ward rounds and referrals easier.
Healthcare software that connects clinical work and protects records

Why it matters
Providers need patient identity, record integrity and access permissions that clinical leaders can trust. Usable workflows and tested continuity arrangements must keep care moving without exposing confidential information.
The problem
Clear screens cannot repair fragmented patient records.
Where clinical workflows lose patient context
Providers need patient identity, record integrity and access permissions that clinical leaders can trust. Usable workflows and tested continuity arrangements must keep care moving without exposing confidential information.
The traps
Trap 0101 / 04
Records that disagree
Duplicate identities
Separate patient records fragment clinical context. Define matching, correction and merge workflows.
Trap 0202 / 04
Privacy by assumption
Broad record access
Shared accounts hide who viewed a record. Apply role-based access and retain reviewable access logs.
Trap 0303 / 04
Disconnected handovers
Referrals lose context
Referrals travel without current notes or ownership. Keep the patient context and next action visible.
Trap 0404 / 04
Care without continuity
Untested downtime
An outage removes essential records. Agree fallback workflows and rehearse restoration with clinical teams.
Healthcare, in figures
The health ministry's November 2025 figures frame capacity, household costs and insurance workflows. Underlying reference years for the ratio and spending share are unspecified; none is a measured Sparkr outcome.
Doctor population ratio
1:5,000
Nigeria's doctor-to-population ratio, not caseload; ministry report, November 2025. Reference year unspecified.
Out-of-pocket health spending
71%
Nigeria's out-of-pocket health spending share; ministry, November 2025. Reference year unspecified.
Health insurance enrolments
>20m
Nigerians enrolled through formal and vulnerable-group insurance programmes; ministry, November 2025.
Breach notification
72h
Notify NDPC within 72 hours of awareness where a breach risks individuals' rights or freedoms; NDPA 2023 / GAID 2025.
Sources: Federal Ministry of Health: workforce, November 2025; Federal Ministry of Health: spending, November 2025; Federal Ministry of Health: enrolments, November 2025; NDPC, NDPA 2023 / GAID 2025 (72-hour risk-based notification).
03
Public sources behind the figures on this page
- 01Federal Ministry of Health: workforce, November 2025
- 02Federal Ministry of Health: spending, November 2025 and related sector figures
- 03NDPC: GAID 2025 and breach notification
Figures retain their source periods and scope. They describe sector conditions and legal duties, not Sparkr project outcomes.
How we work with your team
Start with the workflow, then test the controls
We map patient identity, clinical tasks and record access. Together we agree owners, acceptance criteria and the evidence needed before delivery starts.
Step 01
Scope & Discovery
We map critical tasks, system boundaries and risk with your delivery and operational owners.
Step 02
Architecture & Controls
We define access rules, data flows and failure handling before implementation decisions are fixed.
Step 03
Workflow Design
We prototype critical tasks and review them with users before building the full workflow.
Step 04
Build & Test
We implement in reviewed increments, testing permissions, integrations and exception handling.
Step 05
Release & Operational Handover
We agree release checks, recovery procedures and support ownership, then hand over evidence.
Selected work
Related work and delivery capabilities
- Operational workflows
- Access reviews
- Reconciliation
- Audit evidence
- Recovery planning
Services
The services we bring to this sector.
How do you scope healthcare work?
We start with the workflow, system boundaries and the evidence your team needs. The scope records users, integrations, data categories, access roles, operational risks and acceptance criteria. We then agree delivery phases and commercial terms. We do not publish a fixed price before reviewing complexity, dependencies, migration needs and the controls that must be tested.
Can you work with our existing systems?
We review available APIs, data ownership and integration constraints before proposing changes. The plan includes failure handling, reconciliation where relevant and a staged release. We agree what stays, what changes and who owns each dependency rather than assuming a full replacement is necessary.
How do you protect sensitive records?
We define role-based access, encryption needs, data handling rules and audit trails with your owners. Test environments should use appropriate masked or synthetic data. Retention, exports and privileged access need explicit decisions, not default permissions.
Can you help us evidence our obligations?
We help translate applicable requirements into controls, workflows and reviewable evidence. Your compliance and legal teams confirm applicability. Delivery may include access reviews, incident records and control tests; it does not constitute regulatory approval or a guarantee of compliance.
How do you agree delivery timescales?
Timescales follow scope, integration access, data quality and review availability. We agree milestones after discovery, with clear acceptance criteria and dependency owners. A staged release can prioritise essential workflows without hiding unfinished controls.
What related work can we review?
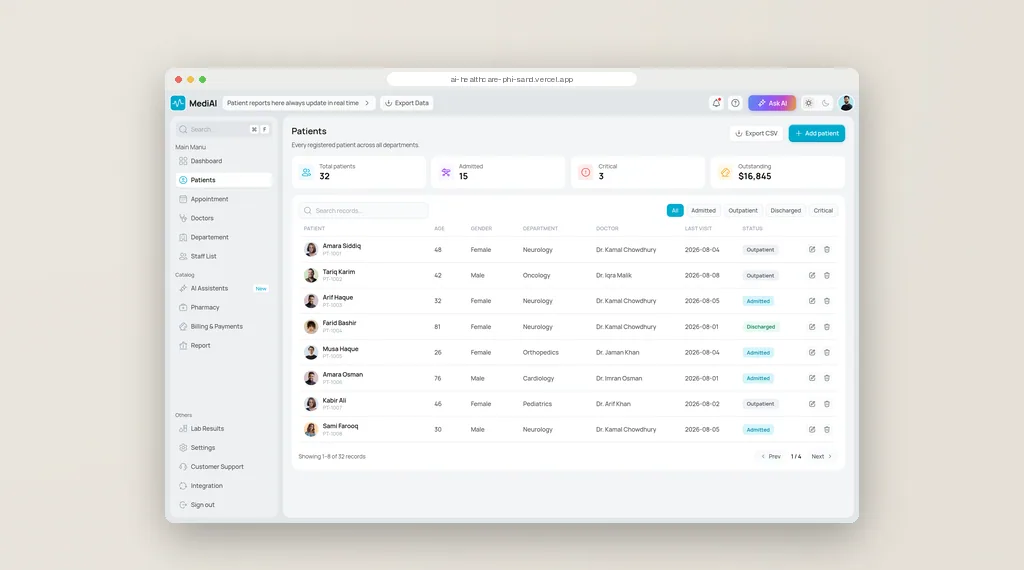
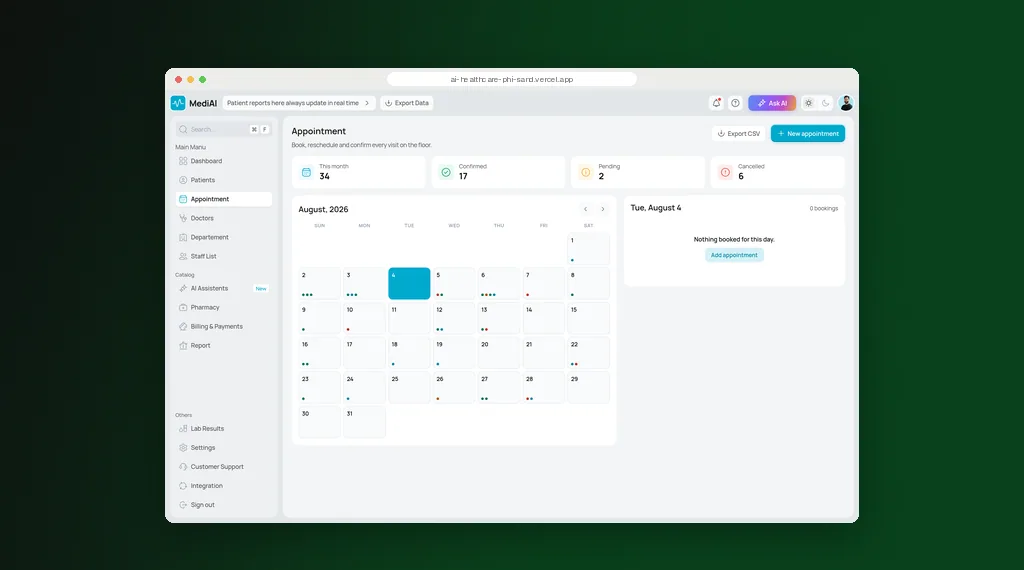
MediAI is an interface design and prototype for a clinical workspace. Its demo opens at sign-in. It demonstrates information hierarchy, not clinical effectiveness, diagnostic accuracy, regulatory compliance or readiness for patient care.
Software development as a service, or a fixed project? How to choose
5 min read
A continuing backlog and a fixed delivery scope need different commercial arrangements. Compare ownership, acceptance criteria and engineering cadence before deciding how to engage.
The 72-hour clock: what NDPA and the GAID demand of your systems
6 min read
Notification depends on risk to individuals, not simply an incident label. Prepare the access logs, incident ownership and assessment records needed to act within the statutory window.
What a regulator-ready VAPT report contains
6 min read
Written authorisation, scope, reproducible findings and retest evidence make a security assessment useful. See what risk teams need beyond an automated list of vulnerabilities.
Designing internal tools people actually use
5 min read
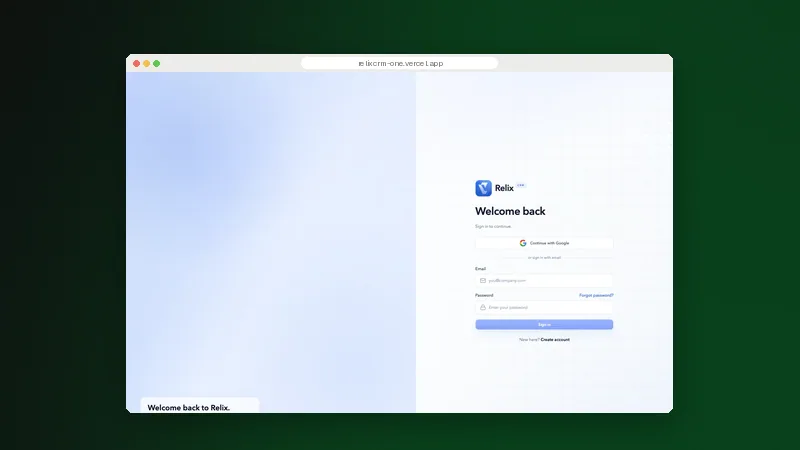
Relix CRM, Victora and Interoly show different contexts for operational work. Start with real tasks, information hierarchy and reviewable decisions rather than adding another dashboard.
What the CBN's baseline standards for automated AML mean for your stack
7 min read
The final 10 March 2026 standards set different implementation windows for DMBs and OFIs. Review monitoring, case management, integrations and the evidence your roadmap needs.
Other industries
Back to all industries